


Resources are used to group users. For example, you can create separate resources for different web projects or departments.
The number of resources you can create depends on your Service Plan. To create additional resources, upgrade or customize your Service Plan.
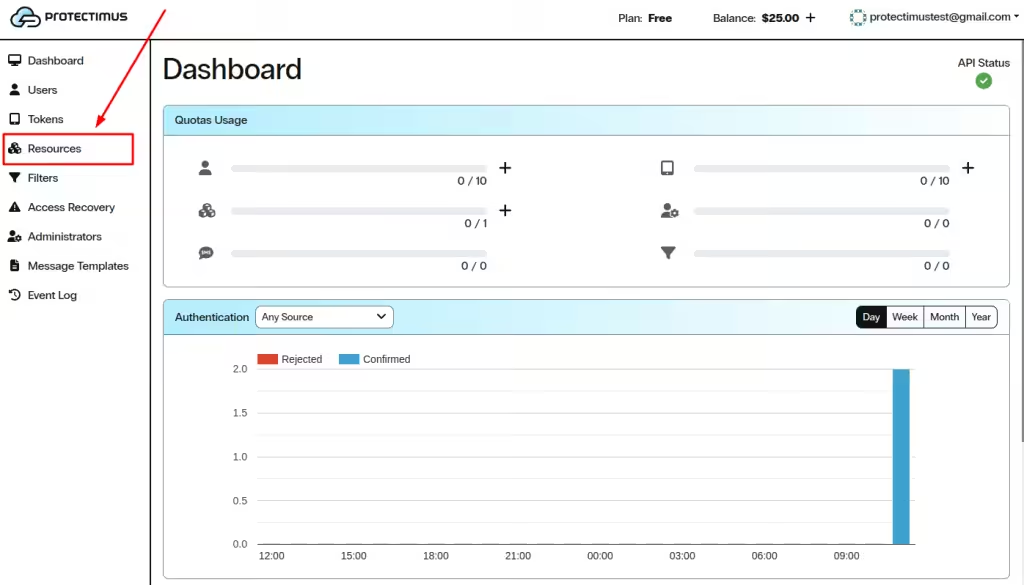
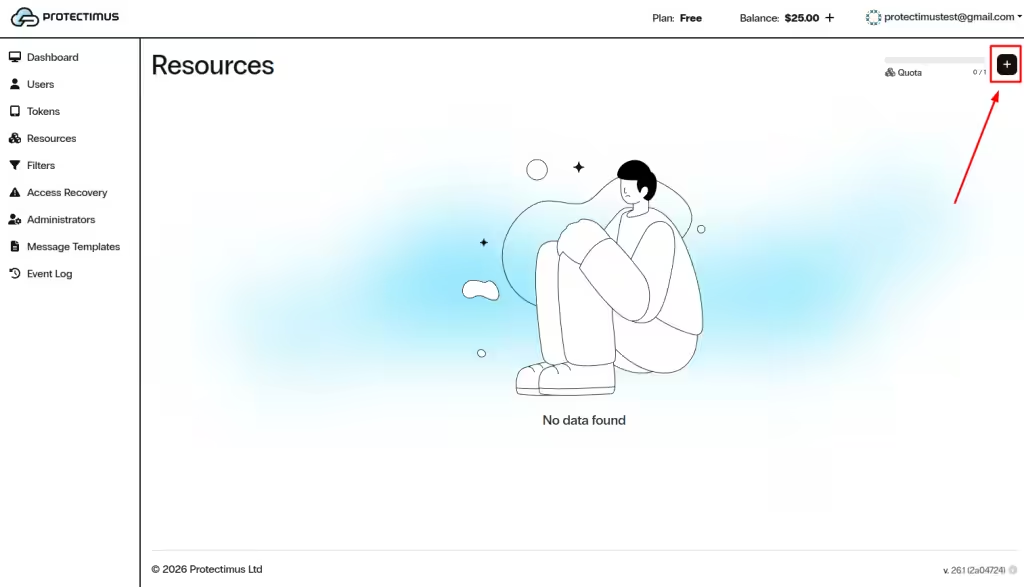
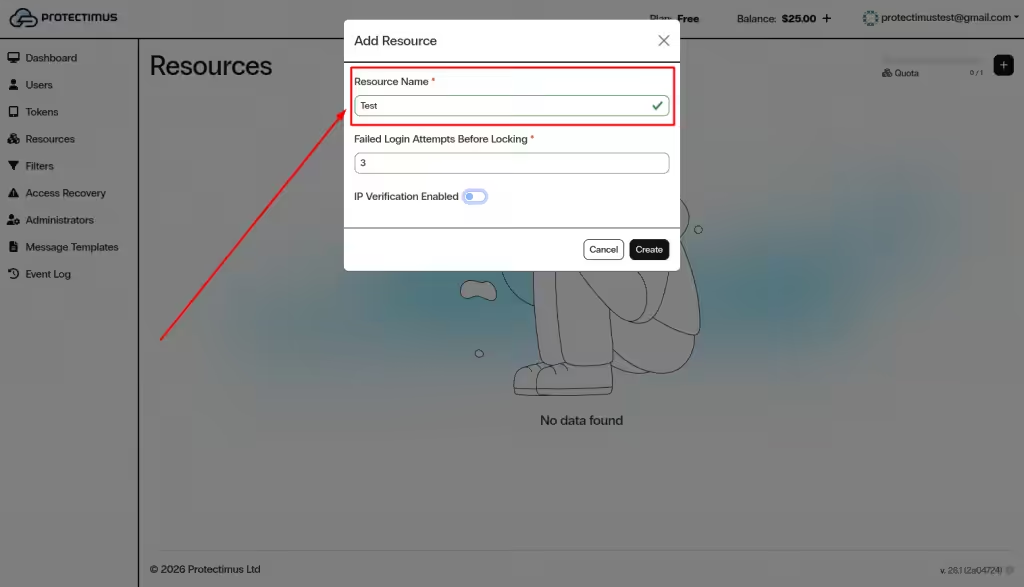
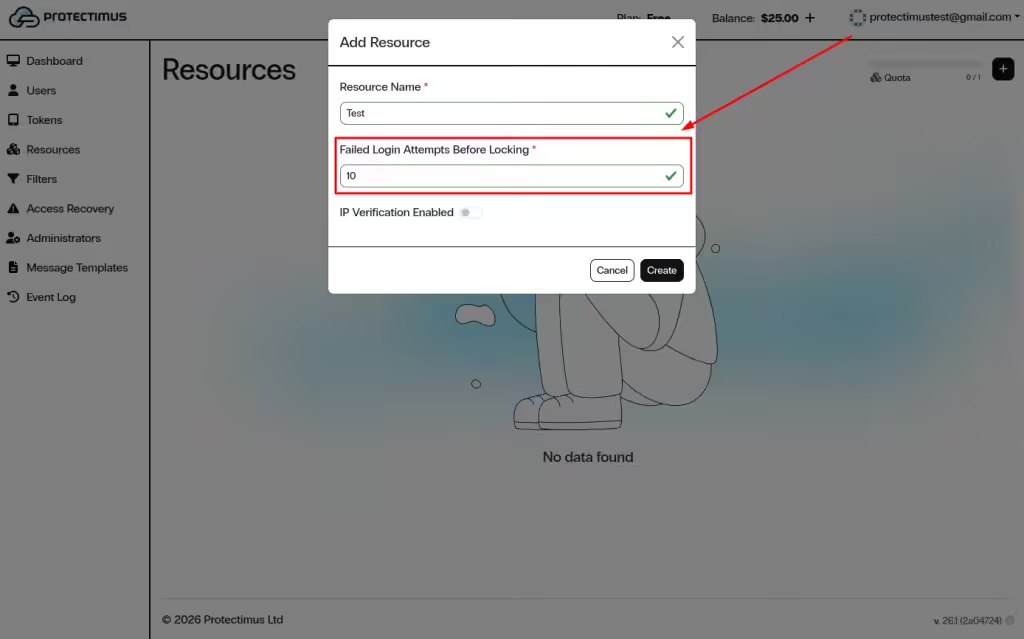
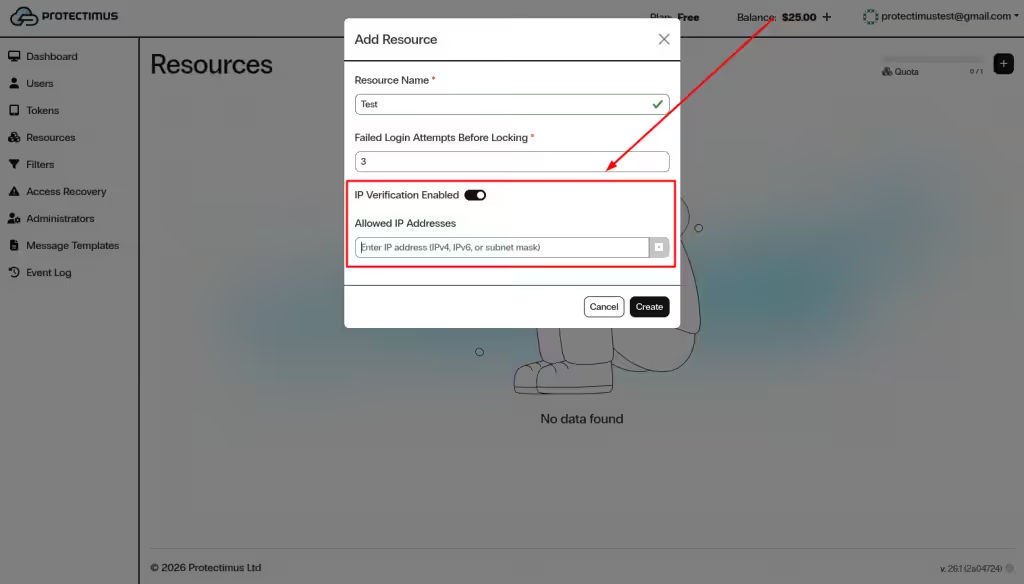
You can also configure the following optional settings:
Failed Login Attempts Before Locking
IP Verification
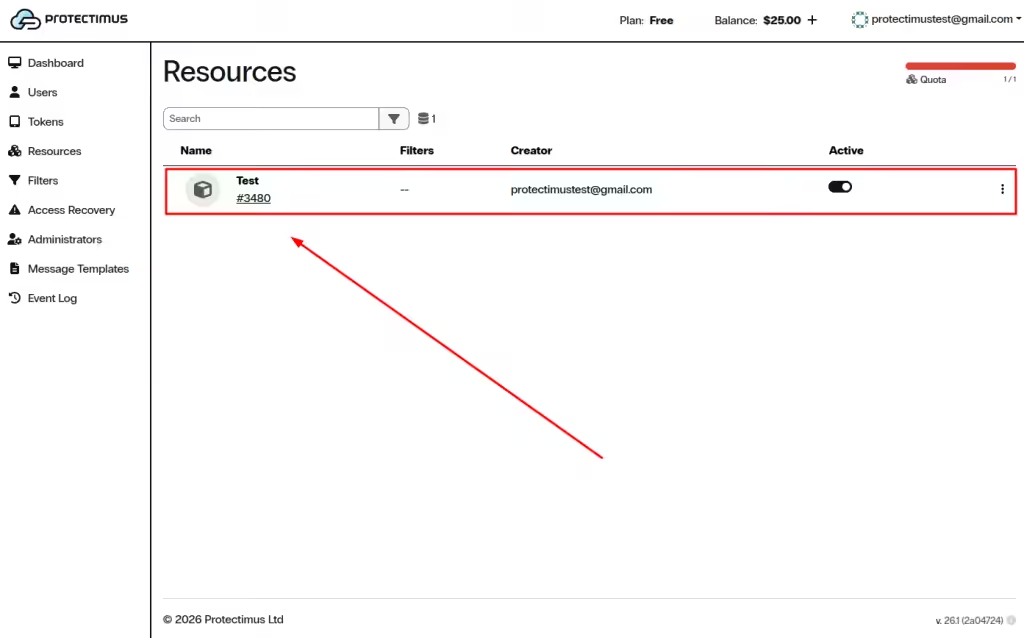
After creating a resource, open its dashboard to configure settings and manage access.
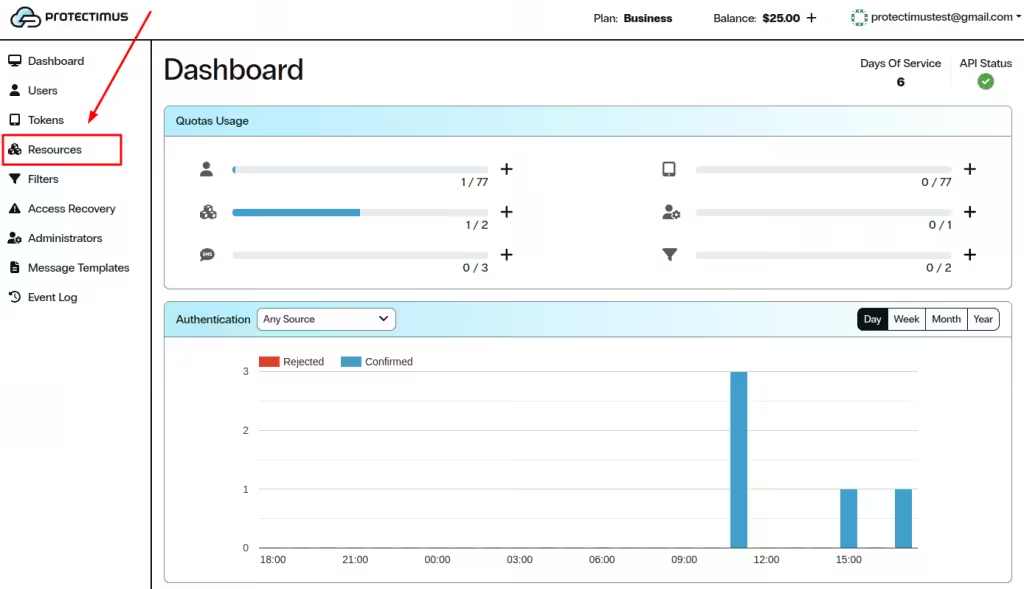
To open the dashboard, go to the Resources page and click the name of the required resource.
The Resource Dashboard includes the following sections:
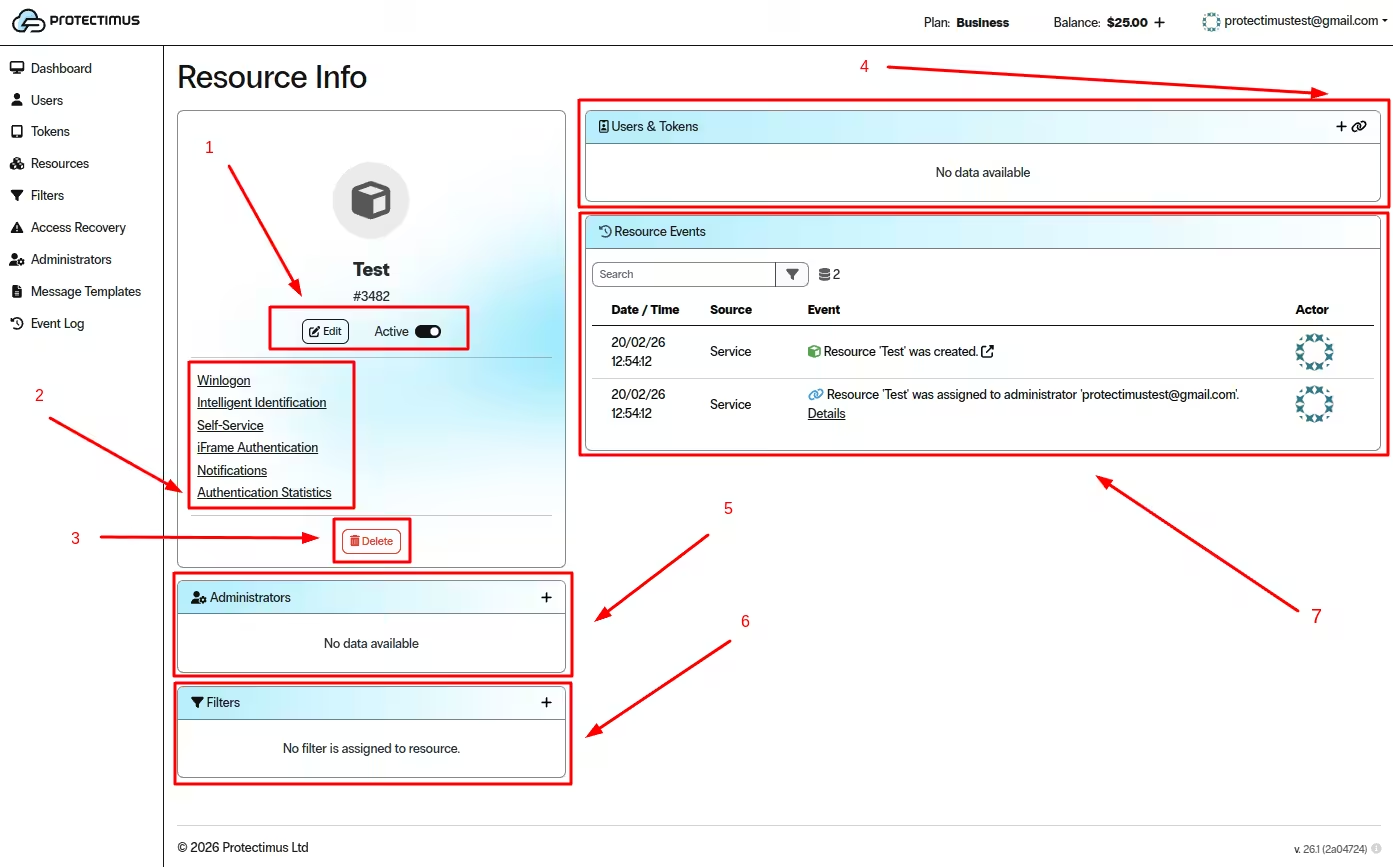
Use the following sections to configure features and view statistics:
Click any section to configure its settings.
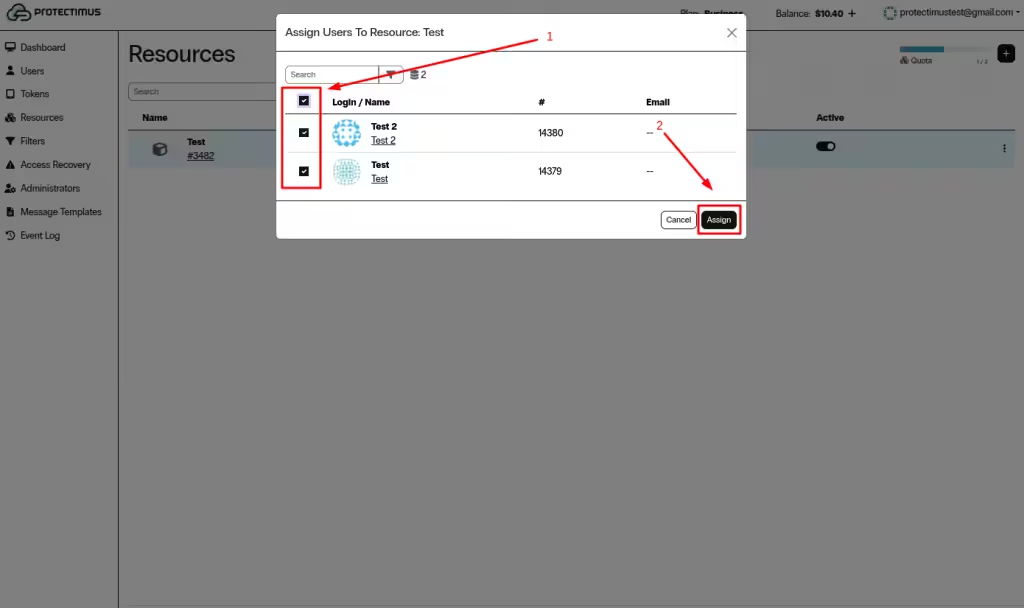
Users and Tokens must be assigned to the Resource. Otherwise, Users will not have access, and Tokens will not work.
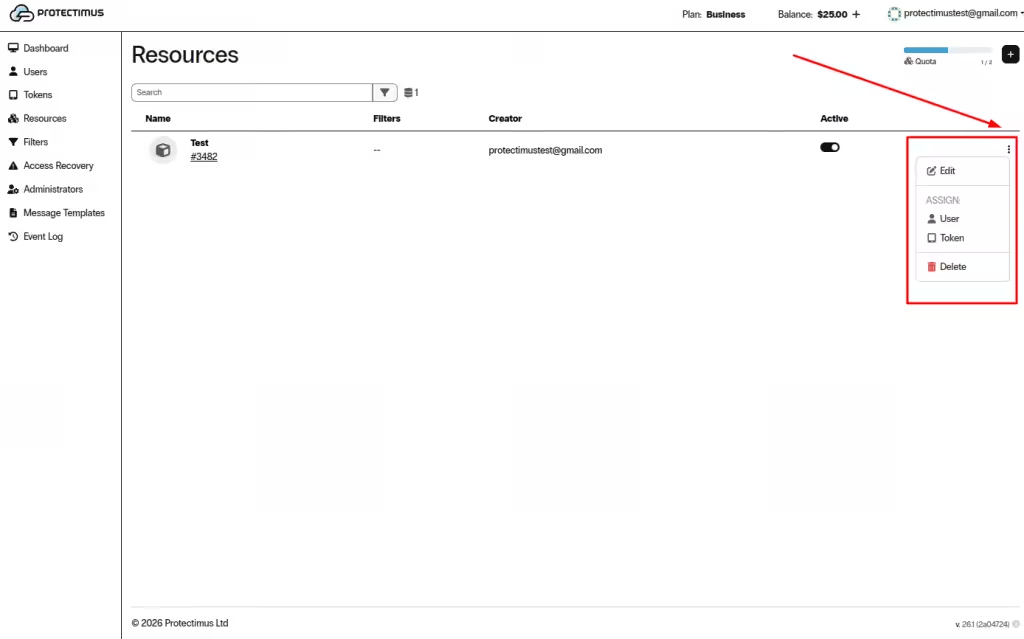
Users and Tokens must be assigned to the Resource, otherwise Users will have no access to this Resource and Tokens won’t work. Protectimus supports several user authentication methods:
- User authentication with a static password. This method requires that a User should have a password, and that this User should be assigned to the Resource.
- User authentication with a one-time password. This method requires that a User should have a Token, this Token must be assigned to the User, and both this User and the Token should be assigned to a Resource.
- User authentication with a static password and a one-time password. It is a combination of the two methods described above. This method requires that a User should have a Token, this Token must be assigned to the User, and both this User and the Token should be assigned to a Resource. If a User’s Token is deactivated, OTP authentication will not be performed, in which case only this User’s static password and this User’s compliance with the filters’ requirements, if any, will be authenticated.
- Token authentication on a resource. This method allows you not to assign a Token to any specific User, but simply to verify the validity of a one-time password generated by the Token. This method requires that a Token should be assigned to a Resource.
If you have any questions, please contact Protectimus customer support service.








