Windows Logon & RDP: Two-Factor Authentication Setup (SaaS Service)
Windows Logon and Remote Desktop Protocol (RDP) are among the most common entry points into corporate infrastructure. If these access points are protected only by passwords, attackers can gain access using credential theft, brute-force attacks, or phishing.
Adding
two-factor authentication (2FA) significantly improves Windows security by requiring users to verify their identity with a one-time password (OTP) or authentication notification.
This guide explains how to enable
two-factor authentication for Windows Logon and RDP using the
Protectimus SaaS Service. It covers configuration in the Protectimus console, Winlogon settings, installation of the Winlogon client, and recommended security policies.
You will also learn how to configure automatic token enrollment, enable offline access with backup codes, and manage authentication policies for both local and remote logins.
Quick Navigation
Windows Logon 2FA Setup Overview
To protect Windows Logon and RDP access with two-factor authentication, complete the following steps:
- Create a Protectimus SaaS Service account.
- Create a Resource in Protectimus.
- Add users and assign tokens, or enable automatic registration.
- Configure Winlogon authentication policies.
- Install the Protectimus Winlogon client.
- Test authentication for both local Windows logon and RDP access.
The sections below explain each step in detail.
Why Protect Windows Logon and RDP with MFA?
- Protects against stolen or leaked passwords
- Helps prevent brute-force attacks on RDP
- Secures administrator access to Windows servers and workstations
- Helps meet internal security and compliance requirements
- Reduces the risk of unauthorized access and ransomware incidents
The Protectimus Windows Logon & RDP solution adds two-factor authentication (2FA / MFA) to protect access to computers running Windows locally and over RDP.
This guide covers the setup process for Protectimus SaaS Service with the updated interface.
If you use the Protectimus On-Premise Platform, please refer to the existing guide: Windows Logon & RDP: Securing Access with Two-Factor Authentication.
The solution supports:
- Windows 8;
- Windows 8.1;
- Windows 10;
- Windows 11;
- Windows Server 2012;
- Windows Server 2016;
- Windows Server 2019;
- Windows Server 2022.
Protectimus can secure both local Windows logon and RDP access. It also supports offline access using backup codes.
For additional information, visit the Protectimus Windows and RDP 2FA Solution page.
1. Register in Protectimus SaaS Service and Prepare the Resource
Create an account in the
Protectimus Cloud Service and activate API.
Then create a Resource, add users, and assign users and tokens as needed. Detailed instructions are available in these guides:
2. Open Winlogon Settings
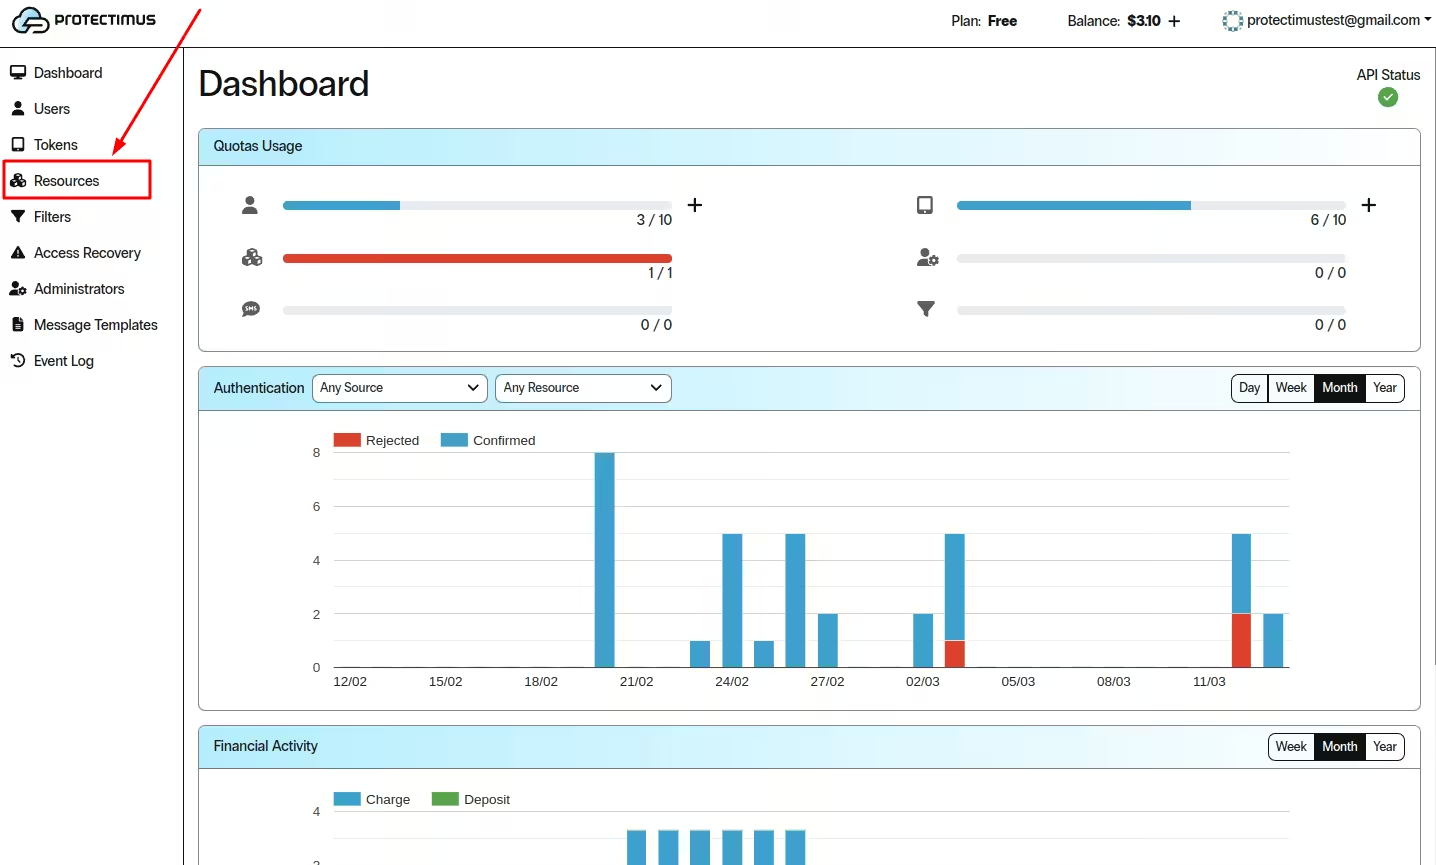
- In the left-side menu, click Resources.
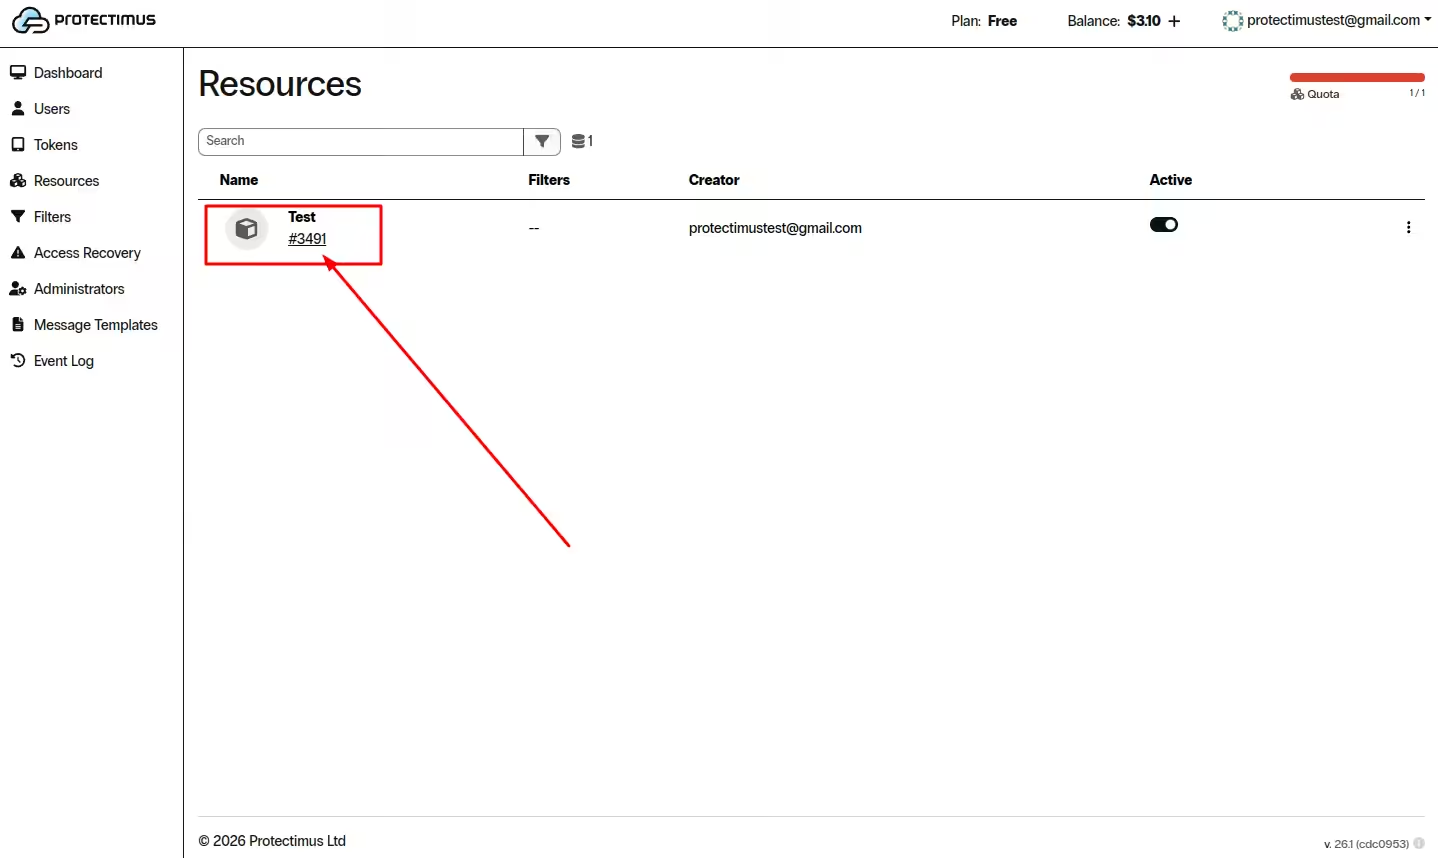
- On the Resources page, click the name of the required Resource.
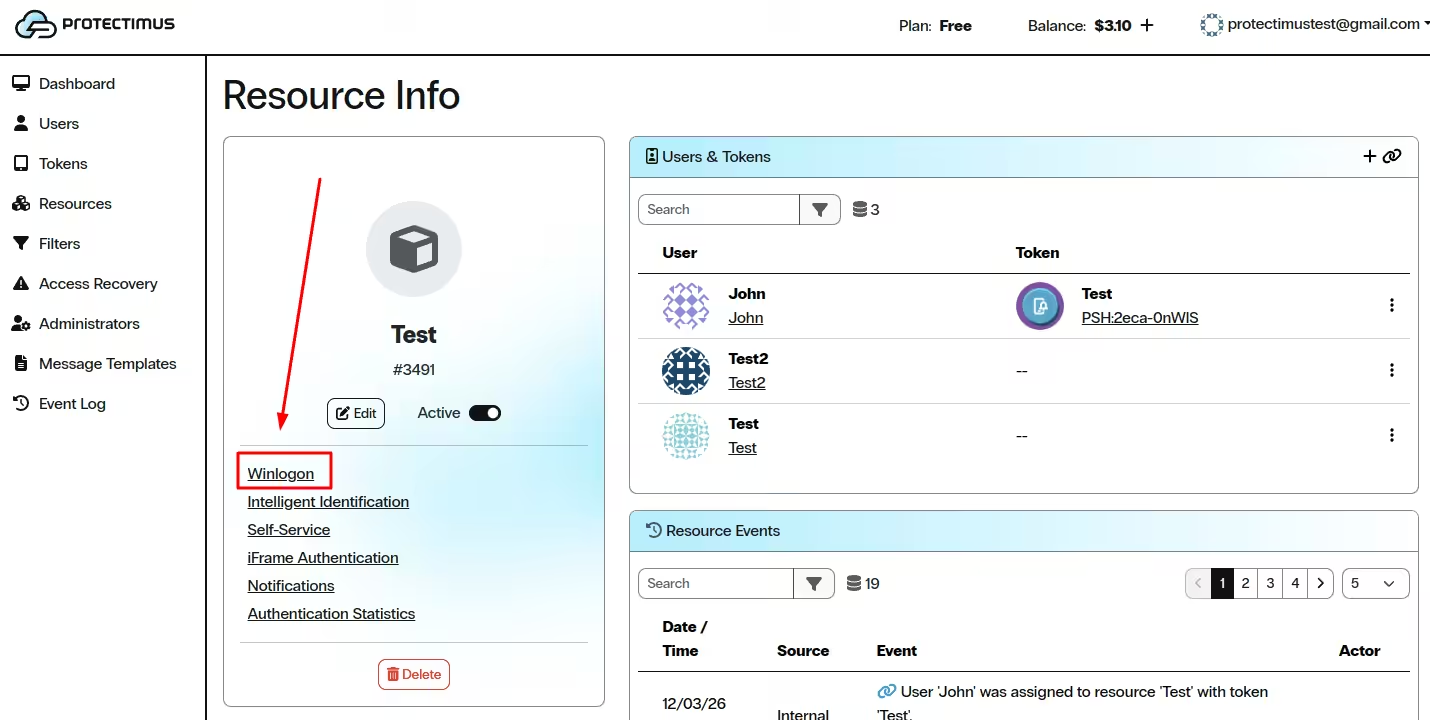
- On the Resource page, click Winlogon.
3. Configure Winlogon Settings
The
Winlogon Settings window contains four tabs:
General,
Local,
RDP, and
Offline.
3.1. General
On the
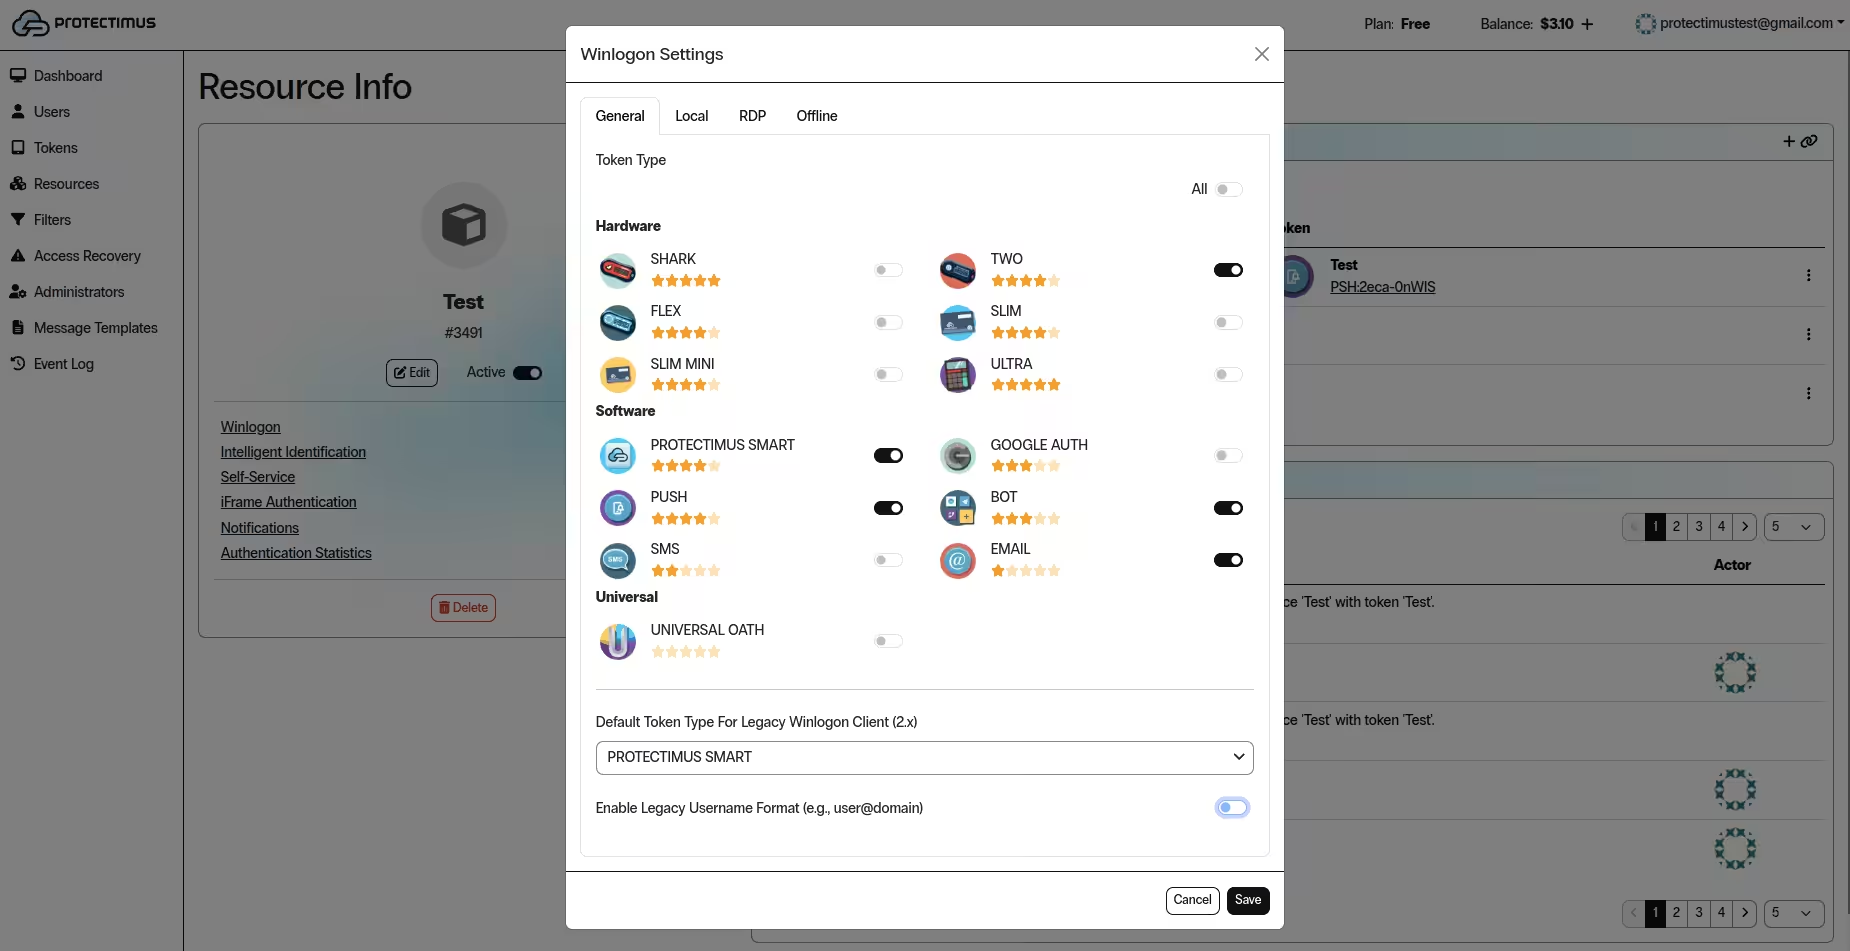
General tab, choose which token types can be used with Protectimus Winlogon.
- Token Type — Select the token types that will be available for Protectimus Winlogon.
- Default Token Type For Legacy Winlogon Client (2.x) — Select the token type for older Winlogon client versions.
- Enable Legacy Username Format (e.g., user@domain) — Enable this option if you need the legacy username format.
We strongly recommend enabling only the token types that are actually required for your deployment.
3.2. Local
On the
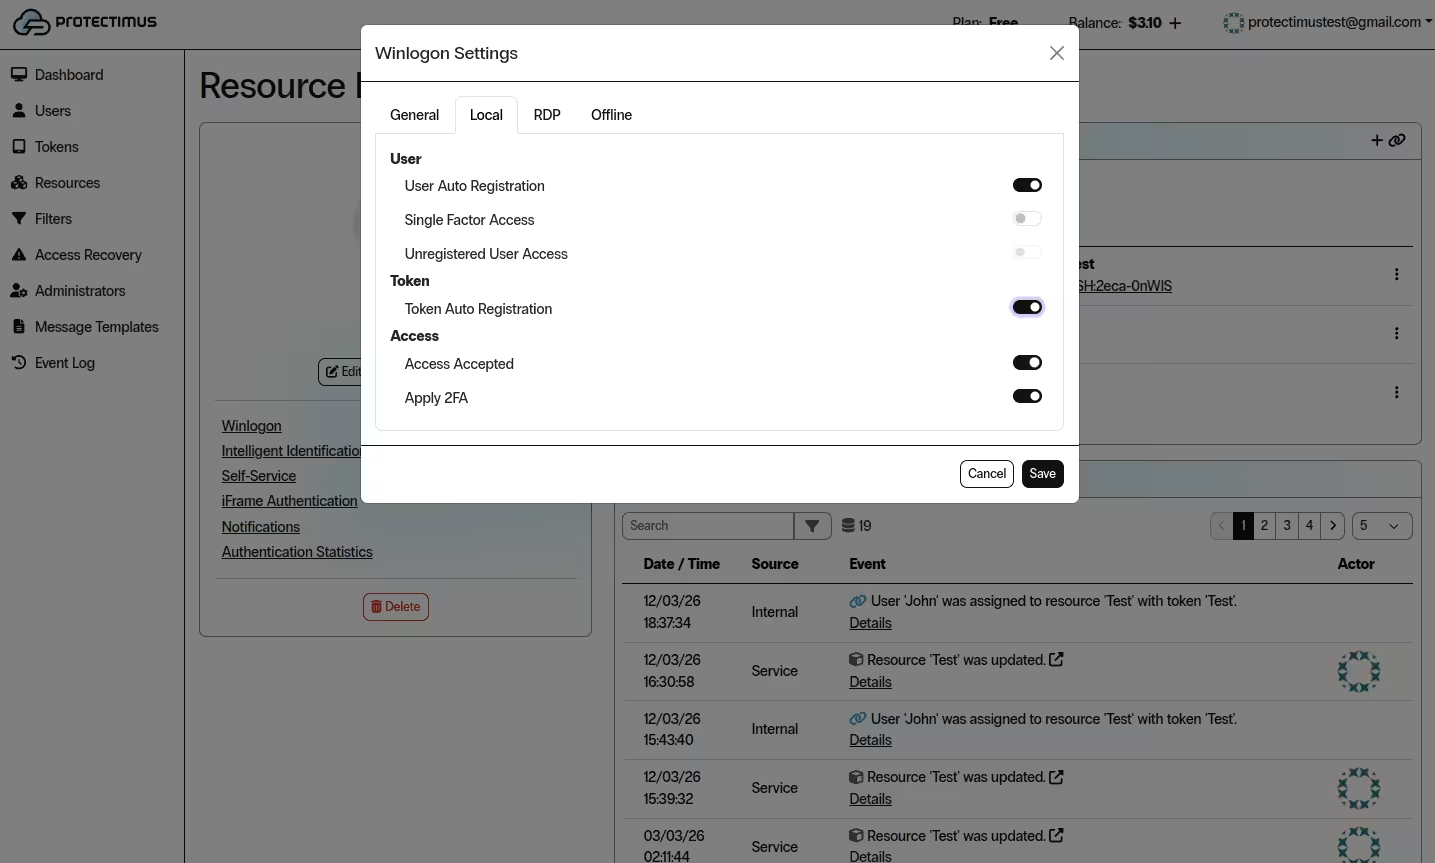
Local tab, configure how users authenticate when signing in directly on the Windows computer.
- User Auto Registration — Automatically creates a user in Protectimus during the first successful Windows sign-in.
- Single Factor Access — Allows users without an assigned token to log in without OTP.
- Unregistered User Access — Allows users who are not registered in Protectimus to sign in.
- Token Auto Registration — Prompts users to enroll a token during first sign-in.
- Access Accepted — Allows local access to the computer.
- Apply 2FA — Requires two-factor authentication for local sign-in.
For most deployments, we recommend enabling
User Auto Registration,
Token Auto Registration,
Access Accepted, and
Apply 2FA.
3.3. RDP
On the
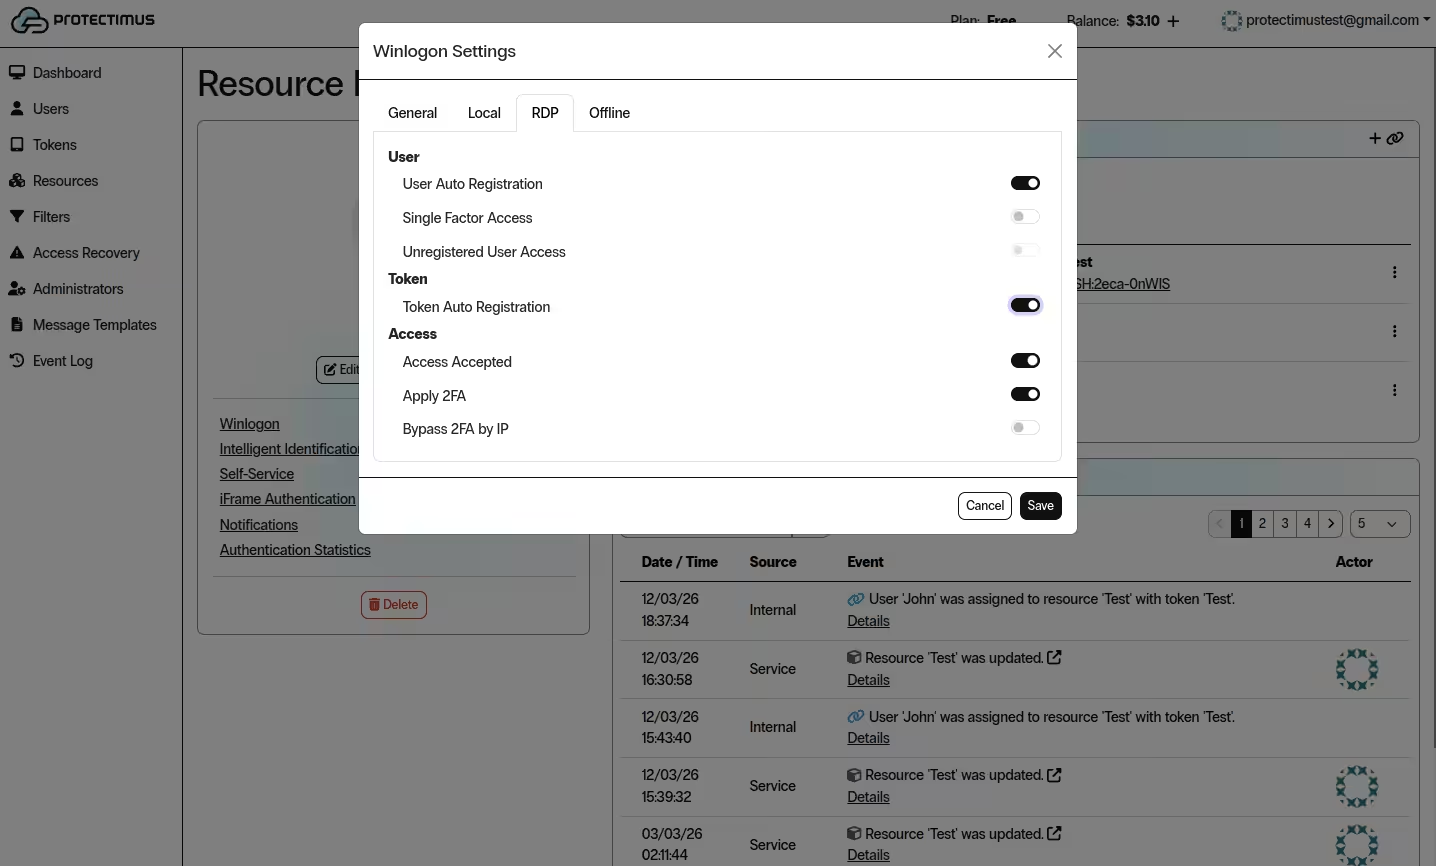
RDP tab, configure how users authenticate when connecting over Remote Desktop Protocol.
- User Auto Registration — Automatically registers users on first RDP sign-in.
- Single Factor Access — Allows sign-in without OTP for users without assigned tokens.
- Unregistered User Access — Allows users not registered in Protectimus to sign in.
- Token Auto Registration — Prompts users to enroll a token during first RDP sign-in.
- Access Accepted — Allows access over RDP.
- Apply 2FA — Requires OTP for RDP sign-in.
- Bypass 2FA by IP — Allows bypassing OTP for trusted IP addresses, if applicable to your policy.
PLEASE NOTE! RDP access is denied until Access Accepted is enabled on the RDP tab.
To protect RDP with two-factor authentication, enable both
Access Accepted and
Apply 2FA.
3.4. Offline
On the
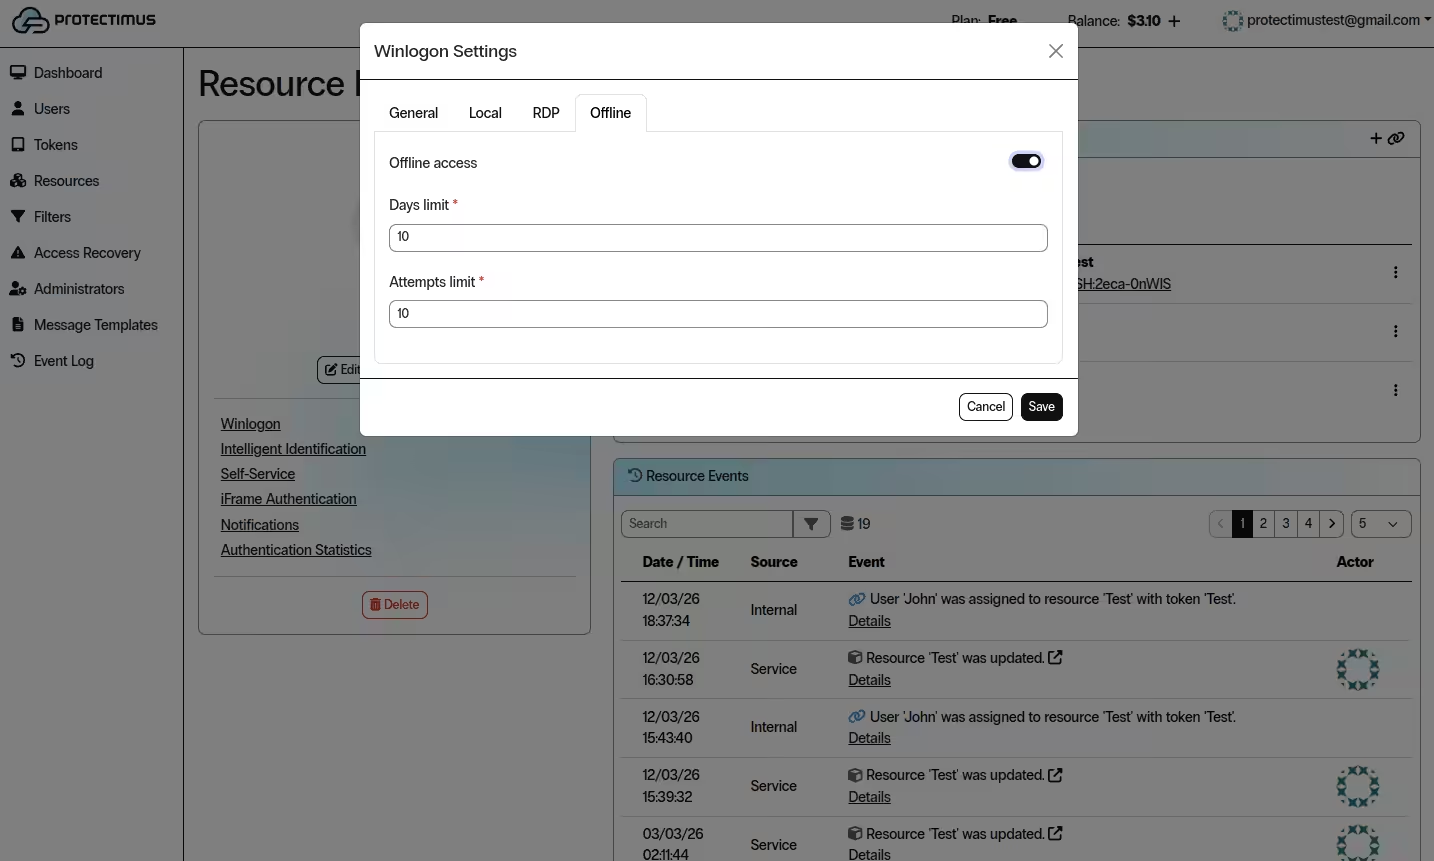
Offline tab, configure backup access when the computer has no Internet connection.
- Offline access — Enables offline authentication.
- Days limit — Defines how many days offline access remains available.
- Attempts limit — Defines how many offline login attempts are allowed.
If offline access is enabled, users can sign in with a backup code instead of a one-time password when the computer cannot connect to the Internet.
4. Recommended Policy for Automatic Enrollment
If you want users to enroll their own tokens during first sign-in, use this recommended setup:
- Enable User Auto Registration;
- Enable Token Auto Registration;
- Enable Access Accepted;
- Enable Apply 2FA;
- Enable only the token types you want users to enroll on the General tab.
This configuration allows users to log in with their usual Windows credentials first and then complete token enrollment automatically.
PLEASE NOTE! You may use different settings for local Windows logon and for RDP access.
5. Add Users and Tokens Manually, If Needed
If you do not want to use automatic registration, add and assign users and tokens manually.
ATTENTION!
The user login in Protectimus must match the Windows username format expected by your environment.
For local Windows accounts, the login in Protectimus should match the Windows username exactly.
For Active Directory environments, usernames may need to use the form login@domain, depending on your configuration.
6. Install Protectimus Winlogon
6.1. Download the Installer and Complete the Initial Setup
- Download the latest version of the Protectimus Winlogon installer.
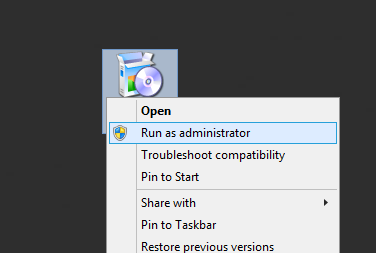
- Run the installer as administrator.
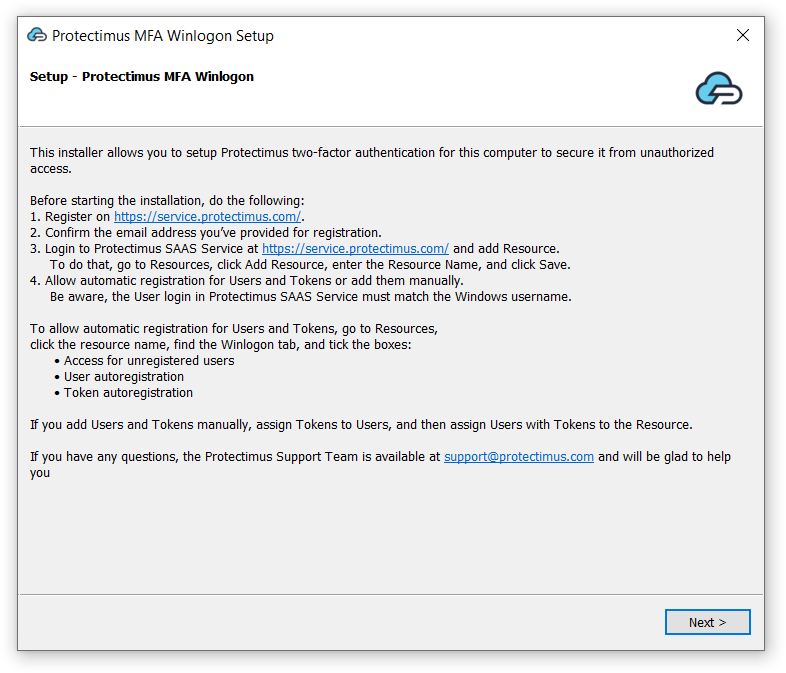
- You will see a welcome screen. Click Next to continue.
- Read the license agreement, select I accept the license, and click Next.
6.2. Enter API URL, Login, API Key, and Choose Resource ID
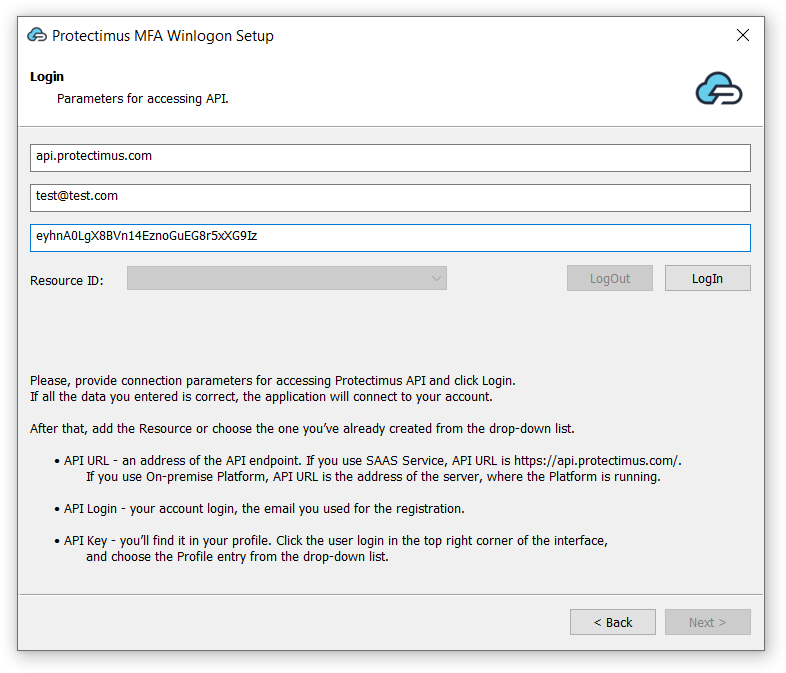
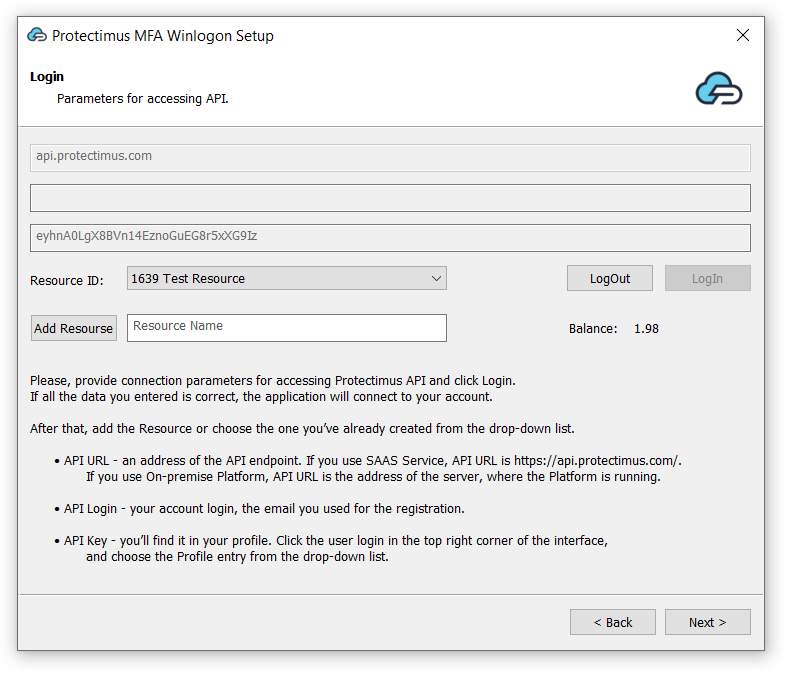
- Enter API URL, Login, and API Key, then click LogIn.
- In the Resource ID field, choose the Resource you configured earlier, then click Next.
These parameters mean:
- API URL — For SaaS Service, use https://api.protectimus.com/.
- Login — Your Protectimus account login.
- API Key — Available in your profile.
If you have not added the Resource yet, create it first in Protectimus SaaS Service.
6.3. Configure 2FA Policy and Save the Backup Code
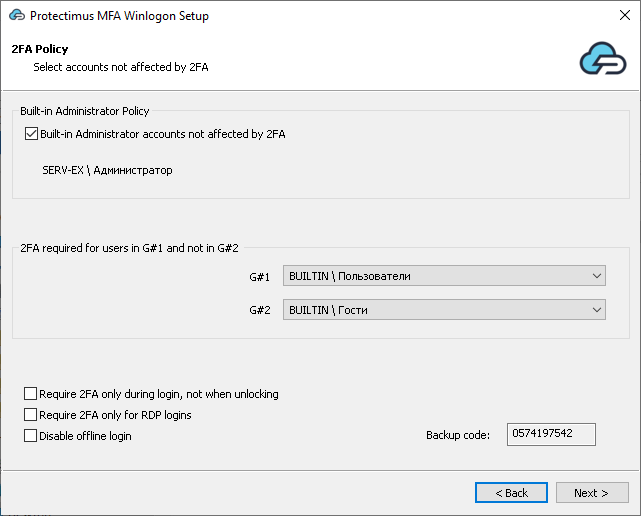
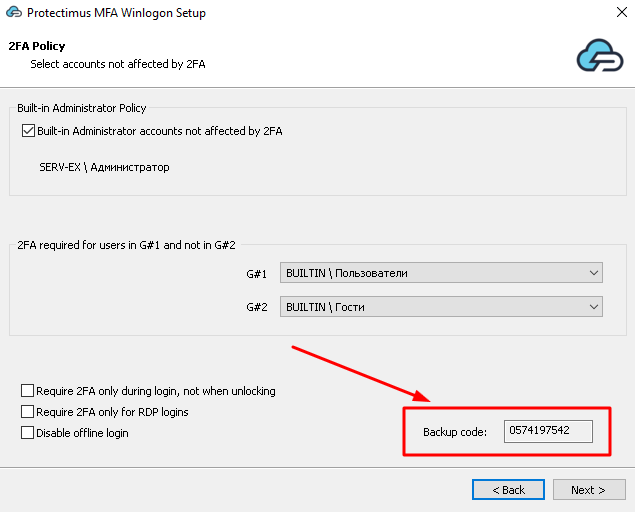
Configure the 2FA policy and save the backup code if needed. By default, two-factor authentication is applied to all accounts on this computer except the built-in Administrator and guest accounts.
- You can enable 2FA for the built-in Administrator or for a group of users.
- You can configure additional settings such as:
- Require 2FA during login, not when unlocking;
- Require 2FA only for RDP logins;
- Disable offline login.
- You can save the backup code. Users can use this code to log in when there is no Internet connection.
ATTENTION!
When a backup code is used, a new one is generated. Save the new code for the next offline login. The backup code works for all accounts on the same computer.
6.4. Choose Domain Installation Options
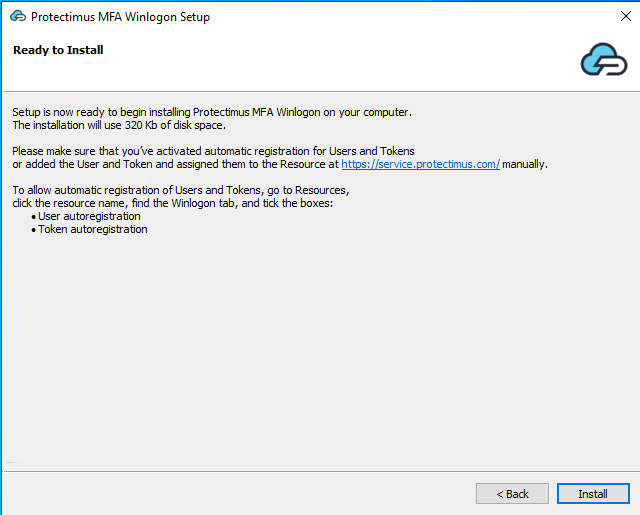
If this is
not a domain controller, just click
Install.
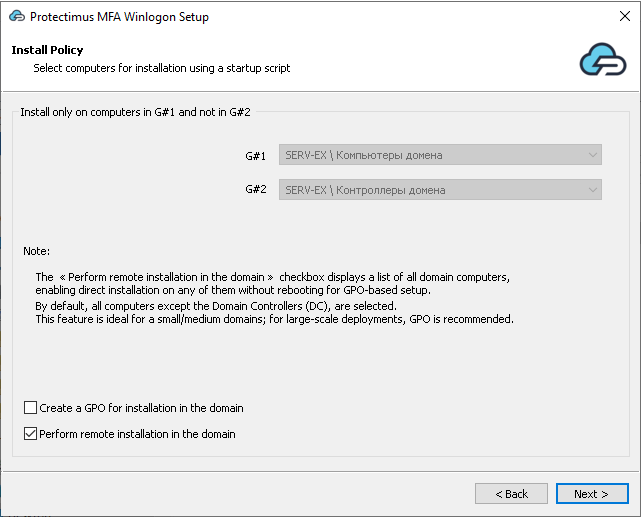
If you install Protectimus Winlogon & RDP 2FA on a
domain controller, you will see two additional options:
- Create a GPO for installation in the domain — Creates a Group Policy Object for automatic installation on domain computers.
- Perform remote installation in the domain — Opens a window for direct installation on selected domain computers.
6.5. Finish the Installation
After the installation is completed, click
OK. Two-factor authentication will be enabled the next time the computer starts.
7. Backup Codes for Offline Access
For Protectimus Winlogon to work normally, the computer must be connected to the Internet.
If the Internet connection is unavailable, users can sign in with a backup code instead of a one-time password.
The first backup code is issued during installation. This code is valid for all accounts registered on the same computer. It can be used only once. After that, a new backup code is generated.
ATTENTION! When a user logs in with a backup code, a new code is generated. Save it for the next offline login. The new code is also valid for all accounts on this computer.
7.1. How to Reissue a Backup Code
If users lose the backup code, they can generate a new one while online. For this, your chief Protectimus account administrator should request a special utility from
support@protectimus.com.
To use the utility:
- Sign in to Windows.
- Download and run the utility.
- Press CTRL + ALT + DEL.
- Save the new backup code.
8. Logs and Errors
If you encounter problems, first check the Windows system logs:
Event Viewer → Windows Logs → Application.
You can also review relevant events in your Protectimus account.
9. Uninstalling
If there is no access to the Windows account, you can disable the Protectimus Winlogon application in Safe Mode.
- Open the Windows Uninstall or Change a Program menu, find Protectimus Winlogon, and click Uninstall.
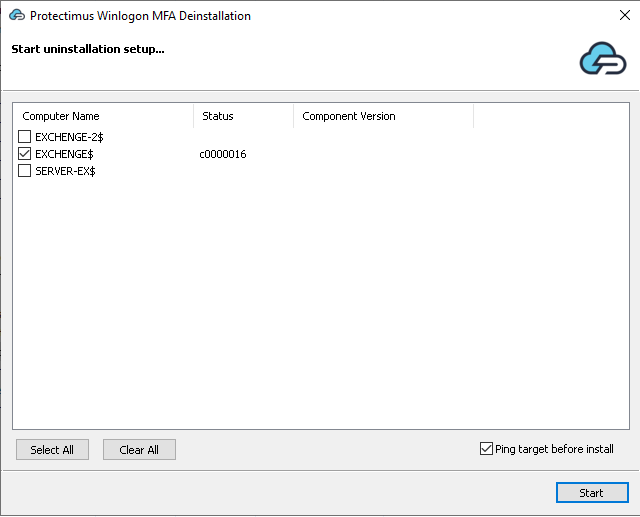
- If this is a domain installation, the Start uninstallation setup window will open. You can use the same approach as remote installation during deployment.
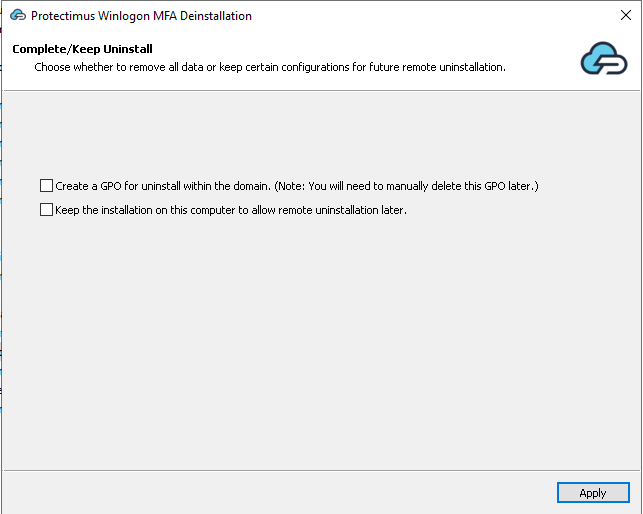
- After closing the previous window, the Complete/Keep Uninstall window will open, where you can:
- Create a GPO for automatic uninstallation on domain computers;
- Keep the component on the current computer for future uninstallation tasks.
ATTENTION!
If you create a GPO to uninstall Protectimus Winlogon & RDP on all machines in your domain, delete this GPO manually after the uninstallation is finished.
If you do not remove the uninstall GPO manually, it may cause problems when you install the component again later.
Frequently Asked Questions
Does Protectimus support Windows Server authentication?
Yes. Protectimus supports Windows Server 2012, 2016, 2019, and 2022, allowing administrators to protect both local logon and RDP access.
Can I protect Remote Desktop (RDP) with two-factor authentication?
Yes. Protectimus Winlogon allows administrators to require one-time passwords for Remote Desktop logins, helping prevent unauthorized access.
What happens if the computer is offline?
If the computer has no Internet connection, users can sign in using a backup code generated during installation.
Does Protectimus support automatic user enrollment?
Yes. Administrators can enable
User Auto Registration and
Token Auto Registration so users can enroll their tokens during the first login.
Which token types can be used for Windows authentication?
Protectimus supports several token types, including mobile OTP apps, hardware tokens, SMS OTP, and messenger-based tokens, depending on your configuration.
Best Practices for Windows MFA Deployment
- Require 2FA for all administrator accounts
- Enable Apply 2FA for both Local and RDP access where possible
- Use User Auto Registration and Token Auto Registration for easier deployment
- Limit the enabled token types to only those required
- Store backup codes securely and update them after each offline use
- Review Windows and Protectimus logs regularly
Related Guides








