Strong Authentication
Classic 2FA / MFA
MFA for AD, LDAP, Databases
Self-Service Password Reset (SSPR)
Wi-Fi Authentication
Electronic Visit Verification
Get Started
Classic 2FA / MFA
API Documentation
Software Development Kits
Programmable hardware TOTP token in a card format that fits any authentication system
Classic hardware TOTP token with SHA-1 algorithm support
Programmable hardware TOTP token in a key fob format that fits any authentication system
Classic hardware TOTP token with SHA-256 algorithm support
Popular Integrations
A free 2FA authenticator app with cloud backup, easy token transfer to a new phone, PIN and biometric authentication protection

Free OTP delivery with chatbots in messaging apps

Delivery of one-time passwords via SMS messages

Free delivery of one-time passwords via email

Free one-time passwords delivery via push notifications

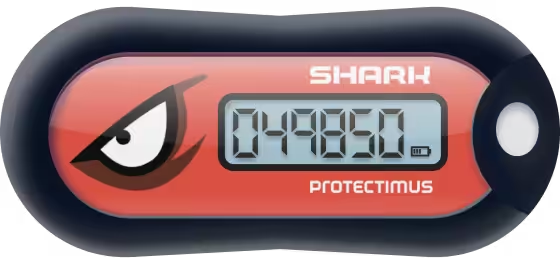
Protectimus provides the infrastructure needed to integrate hardware TOTP tokens into existing Electronic Visit Verification (EVV) systems. EVV platforms can validate one-time passwords through the Protectimus API and determine the time interval associated with each valid OTP.
The solution can be integrated into existing EVV workflows and does not require care recipients to use a smartphone, mobile application, GPS, or Internet connection.
Electronic Visit Verification (EVV) is an approach used to electronically verify information about visits performed by workers providing certain home healthcare and personal care services.
In the United States, EVV requirements apply to certain Medicaid-funded services. EVV systems may record various details about a visit, including the date, start and end times, service recipient and provider, type of service provided, and other information required by applicable regulations.
Specific EVV requirements and acceptable methods of visit verification may vary depending on the program, state, service provider, and EVV platform being used.
Protectimus does not replace a complete EVV system. Protectimus hardware TOTP tokens, API, and validation infrastructure can be integrated into EVV platforms as technical components for verifying visit times.
Using a mobile application or other methods that depend on a smartphone and Internet connectivity is not convenient in every scenario.
A Protectimus hardware TOTP token can remain at the location where services are provided. The token independently generates time-based one-time passwords and does not require an Internet or mobile network connection.
A worker can record the code displayed by the token at the beginning and/or end of a visit and submit it to the EVV system being used.
Through the Protectimus API, the EVV system submits the token identifier and OTP. Protectimus validates the code and returns the corresponding time interval.
This provides the EVV platform with an additional source of time-related data that can be used as part of its visit verification workflow according to its own business logic and applicable requirements.
The hardware token generates one-time passwords using the standard TOTP (Time-Based One-Time Password) algorithm.
Each OTP corresponds to a specific time interval — for example, 30 or 60 seconds, depending on the token configuration.
When an EVV system submits an OTP together with the identifier of the corresponding token, the Protectimus API can validate the code and determine the time interval to which it corresponds.
Important: A TOTP token by itself does not determine geographic location, the identity of the worker, the type of service provided, or whether the service was actually performed. These data, when required, are handled separately by the EVV system.
The EVV provider or service organization assigns a hardware TOTP token to the appropriate care recipient or service location according to its own procedures. The token operates independently and does not require an Internet connection.
At a time defined by the EVV provider — for example, at the beginning of a visit — the worker reads and records the current one-time password displayed by the TOTP token.
A second one-time password may be recorded at the end of the visit. Whether one or multiple codes are required, as well as the specific workflow, is determined by the EVV provider.
The collected OTPs are submitted to the EVV platform using a method defined by the platform provider, either during the visit or at a later time. The EVV system can associate the OTPs with its own data about the worker, care recipient, visit, and services provided.
The EVV platform submits the token identifier and OTP to Protectimus. Protectimus validates the code and, if it is valid, returns information about the corresponding time interval. The resulting data is then processed by the EVV system according to its own business logic.
CareVoyant is an integrated enterprise-level software platform for Home Care Agencies that offers Cloud-based healthcare software for Home Care, Home Healthcare, and Home & Community-Based Services (HCBS).
Protectimus offers hardware TOTP tokens with different OTP lengths and generation periods. For EVV systems where codes may be submitted later, longer OTPs are recommended to reduce the chance of duplicate combinations.
Protectimus TWO generates 6-digit one-time passwords and can be used as a source of TOTP codes for integrated EVV systems. The token operates independently, requires neither a smartphone nor an Internet connection, and is designed for long-term operation. When using 6-digit codes, the EVV platform should take into account the possibility of identical numeric OTP values recurring over longer time periods.
For EVV scenarios, particularly when an OTP may be submitted to the server after a delay, Protectimus offers tokens with 8-digit one-time passwords. The increased OTP length reduces the probability of identical numeric combinations occurring within the relevant time range and makes it easier to associate a code with its corresponding time interval. The specific token configuration should be selected based on the architecture and business logic of your EVV system.
Protectimus provides hardware tokens, API, and TOTP validation infrastructure for integration with existing EVV platforms. OTP validation can be handled via the Protectimus Cloud Service or On-Premise Platform, while all EVV-related data and processes remain within the EVV system.
An EVV platform can integrate with the Protectimus Cloud Service via API. The system submits the data required for token validation and receives the OTP validation result along with the corresponding time interval. Personal or medical information does not need to be transmitted to Protectimus, as token, user, and visit associations can remain within the EVV system. Before using the cloud option, customers should determine the data processing and hosting requirements applicable to their EVV system.
The Protectimus On-Premise Platform can be deployed within the EVV provider’s infrastructure or another environment controlled by the customer. In this case, OTP validation is performed within the customer’s infrastructure. The EVV platform communicates with Protectimus through the API, while the customer determines the architecture for storing EVV data, personal information, and visit information. The Protectimus team provides documentation and technical support for integration.

Hardware tokens do not require a smartphone, mobile application, Wi-Fi, mobile Internet connection, or continuous connection to a server. This makes them suitable for scenarios where the use of mobile devices is inconvenient or unavailable.

TOTP is based on time. By validating an OTP, Protectimus can determine the time interval to which the code corresponds. The EVV platform can use this information together with its own data as part of its visit verification process.

The hardware TOTP token itself does not use GPS, a camera, or a microphone and does not collect medical or other personal information. The relationship between the token, care recipient, worker, and specific visit can be managed entirely by the EVV platform.

Protectimus provides the API and validation infrastructure required to add hardware TOTP token support to an existing EVV system without replacing its underlying architecture.

Depending on project requirements, different TOTP parameters can be used, including OTP length and validity period. The validation infrastructure can be used through the Protectimus cloud service or deployed on-premise within the customer’s environment.